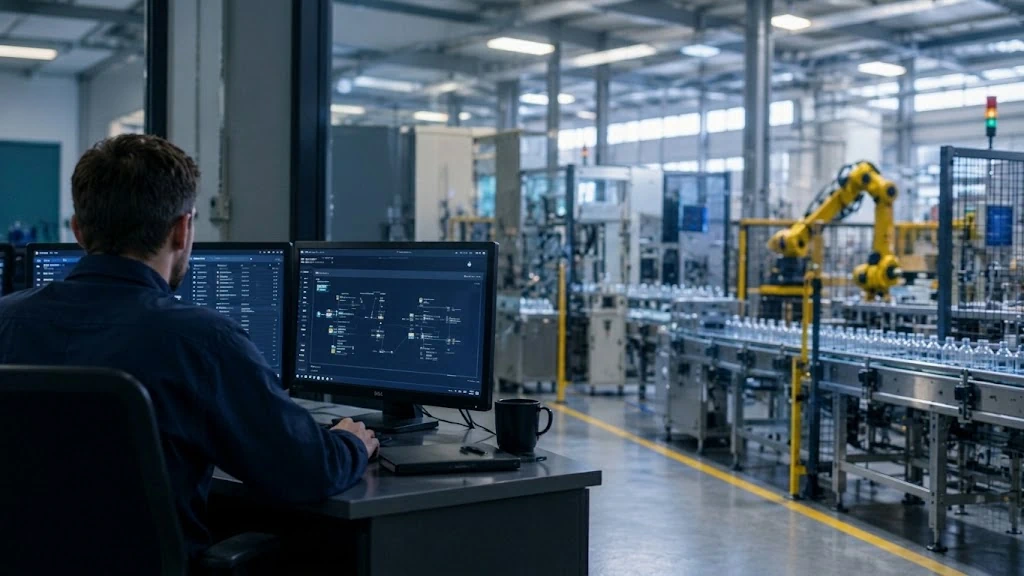
Your office network is only the beginning. Imagine an attacker compromises an employee’s computer. They gain access to your corporate network, identify connected systems and start moving through your environment. How far could they get? Could they reach your engineering workstations? Access production management systems? Disrupt the machinery and processes your production line depends on?
The answer depends on more than the security tools in place. It also depends on how systems connect, what access those connections allow and whether a breach can be contained.
Modern factories rely on interconnected systems, from enterprise resource planning (ERP) platforms to programmable logic controllers (PLCs) and industrial control systems. These connections support efficiency and visibility, but they can also create pathways between business IT and operational technology (OT). If those pathways aren’t properly controlled, a compromise in one area could put others at risk. The question isn’t just whether an attacker can get in. It’s what stops them moving further.
Why manufacturing networks are exposed
Manufacturing businesses face a difficult balance: protecting systems from cyber threats while maintaining the availability, reliability and safety of production. Unlike a typical office computer, industrial equipment may depend on specific software versions, carefully managed maintenance windows or connections to other operational systems. Changes therefore need to be planned around production requirements.
At the same time, legacy equipment, remote supplier access and networks that have evolved over many years can make it harder to maintain a clear picture of the environment. Research from industrial cyber security company Claroty highlights the scale of the challenge. Its State of CPS Security 2025: OT Exposures research analysed almost one million operational technology devices across 270 organisations. The study reported that:
- 12% of the OT devices analysed contained known exploited vulnerabilities.
- 40% of the organisations analysed had some of these vulnerable assets insecurely connected to the internet.
These figures cover the research sample across industries, not manufacturing alone. However, they highlight why manufacturers need to consider both the vulnerabilities affecting their equipment and the connections that could expose it. Identifying vulnerable devices is one part of the picture. Understanding how an attacker could move between them is equally important.
IT and OT: could a breach spread between them?
IT and OT serve different purposes, but modern manufacturing increasingly depends on them working together. IT supports business operations, including email, finance and ERP systems. OT monitors and controls physical processes, machinery and production environments. Connections between the two may be necessary for reporting, production planning, remote maintenance and data exchange. The challenge is ensuring that each connection provides only the access required.
Consider three potential weaknesses:
- Unrestricted access: Could a compromised office device communicate with systems on the production network?
- Remote connections: Could a supplier’s account provide access beyond the equipment they maintain?
- Limited visibility: Would your team know if a device started communicating with systems it doesn’t normally need to reach?
These aren’t necessarily signs of poor security. Manufacturing environments can be complex, and changing established connections requires care. But if you can’t clearly explain how your IT and OT environments communicate, it may be difficult to understand how far an attack could spread.
Network segmentation: limit how far an attacker can travel
Network segmentation divides a network into separate zones and controls how they communicate. For manufacturers, this could mean separating corporate IT from production systems, restricting access to critical equipment and controlling connections between engineering workstations and other operational environments. The objective isn’t to stop every connection. It’s to make sure connections are necessary, authorised and appropriately restricted. Effective segmentation can help manufacturers:
- Restrict access between office and production networks.
- Isolate critical systems to limit the potential spread of a compromise.
- Control remote access for suppliers and maintenance engineers.
- Reduce unnecessary connections between devices and network zones.
The National Cyber Security Centre (NCSC) provides guidance on securing OT connectivity, including reducing exposure and limiting the impact of a compromise. For example, a production sensor may need to communicate with its associated controller. That doesn’t automatically mean it needs unrestricted access to other devices across the network. Segmentation must reflect real operational requirements. Before changing network rules, teams need to understand system dependencies and test changes carefully to avoid disrupting production.
Five questions to ask about your manufacturing network
You don’t necessarily need a complete network redesign to identify potential weaknesses. Start with five practical questions.
1. Do we know what’s connected? Can you account for your IT and OT assets, including older equipment?
2. Can an office device reach production? Understand which routes exist between corporate IT and operational systems.
3. Is remote access restricted? Check that suppliers and engineers can access only the systems they need.
4. Would we spot unusual activity? Consider whether your monitoring can identify unexpected connections or suspicious behaviour.
5. Could we contain a breach? Know how affected systems could be isolated while protecting safety and minimising disruption.
If the answers aren’t clear, reviewing your network architecture and access controls is a practical place to start.
Security tools are only part of the answer
Firewalls, endpoint protection, backups and monitoring platforms all have an important role. But having these tools in place doesn’t automatically mean your environment is secure. The key is understanding how well your controls work together. Without this visibility, it can be difficult to identify unnecessary exposure, prioritise improvements or understand the potential impact of a breach. For teams working with limited time and resources, start with the connections that present the greatest potential risk to critical operations. Map them, review the access they allow and identify where tighter controls or better monitoring could make a difference.
How far could an attacker get?
Manufacturing network security isn’t just about keeping attackers out. It’s also about limiting what they can access if they get in. Could a compromised account reach an engineering workstation? Could a supplier’s connection expose other systems? Would a breach in one area remain contained, or affect wider operations?
The better you understand your network, the better equipped you are to identify weaknesses and limit the potential impact of an attack.
At Syscomm, we work with organisations to understand their networking and security environments, identify potential gaps and develop practical approaches to managing risk. If you’re reviewing your manufacturing network security, start by understanding how your IT and OT systems connect, where access is permitted and which areas need greater visibility or tighter controls. Because before you can address the gaps, you need to know where they are. Find out more about our IT solutions for manufacturing and engineering and get in touch with our team.