- PAST EVENT HIGHLIGHTS
Inside The Next Breach
CRYSTAL MAZE CYBER-SECURITY EXPERIENCE
- Crystal Maze, London
- July 2026
- In-Person Event
Vol. VII
Special Edition
July 2026
Inside
the
NexT Breach
CRYSTAL MAZE CYBER-SECURITY EXPERIENCE
Crystal Maze, London
Syscomm · Strategic Network Solutions
Free Admission
Back Into the Maze, This Time in London
Business leaders returned to the Crystal Maze, this time in London, for a step-by-step look at three real attacks, an honest read on what AI has changed, and the four questions every organisation should be able to answer.
After the success of “Inside the Breach” in Manchester, Syscomm brought the format back to the legendary Crystal Maze, this time in London, for a follow-up built around a simple question: if organisations already own the security tools, why do breaches keep happening?
The morning belonged to Mark Wainwright and Chris Tyler, who had come with a case to make and the evidence to make it. Chris walked the room through three genuine incidents, step by step, in the order the attacker took them: where they got in, what they touched first, and how long they had before anyone noticed. The answer to that last question, it turns out, is twenty-seven seconds. That number did a good deal of work in the room.
Where breaches actually begin
Mark Wainwright opened by clearing the table. Not artificial intelligence. Not nation-state actors. Not zero-days. Whatever the headlines suggest, the incidents Syscomm gets called into rarely begin with anything exotic. They begin with three recurring root causes, all of them ordinary, all of them sitting inside systems the organisation already owns, already pays for, and in most cases believes are working. The rest of the session was spent on the harder part: how each one hides in plain sight, why the usual reporting misses them, and what it actually takes to demonstrate that you do not have them.
The next breach won't be because of AI. It'll be because there's some configuration which isn't correct, some visibility issue, or because nobody validated what they had.
Mark Wainwright - Security Solutions Strategist, Syscomm
What the three attacks had in common
Laid side by side, the three attacks shared the same five weaknesses. Yet not one of those organisations lacked security technology. In every case, the tools needed to stop what happened were already installed and already licensed.
01
The tools are already there
Failures came from configuration, oversight, and monitoring, not a lack of security technology.
02
Attackers used trusted tools
Legitimate software was abused to avoid detection.
03
Backups weren’t enough
They existed, but hadn’t been properly tested for recovery.
04
Warnings were missed
Alerts were generated but not acted on, especially overnight.
05
Third parties increased risk
Suppliers and external partners played a role in every attack.
The unsinkable ship
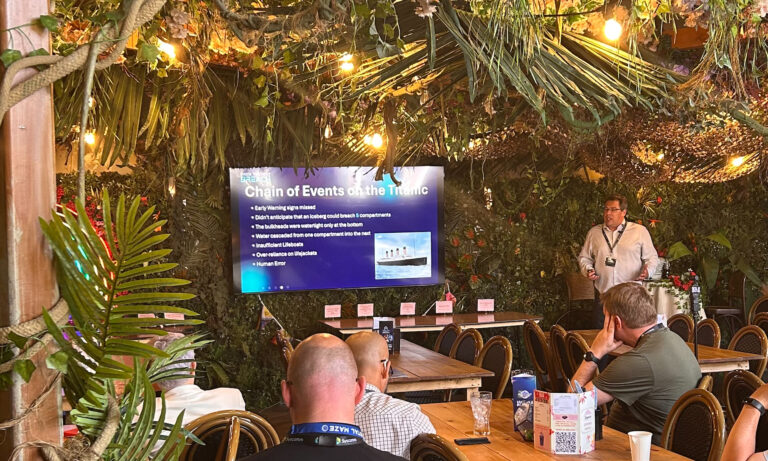
Which raises the obvious question: if the protection was already there, why did none of it hold? To answer it, Chris reached for a ship.
The Titanic was considered unsinkable, with advanced safety measures and a hull divided into watertight compartments, each designed to seal off flooding before it could spread. What sank her was not an absence of protection. It was that a single iceberg breached more compartments than the design had ever anticipated. What Chris drew from that about the average IT estate is on page one of the recap.
What's Actually Changing With AI
AI doesn't unlock a door that was already locked. It just means someone can find the unlocked one a lot faster.
Mark Wainwright - Security Solutions Strategist, Syscomm
Same Attacks, New Scale
AI hasn’t given attackers fundamentally new attack methods — the same core techniques still dominate.
Lower Barrier to Entry
It widens who can attack. More opportunistic and less skilled actors can now run effective attacks.
Accelerated Attack Speed
It compresses reconnaissance & scripting time. What once took analysts days or weeks to find in patched code takes minutes.
Self Assessment
Four Questions Every Organisation Should Be Able to Answer
Can we prove our firewall is configured correctly?
Can we prove attackers cannot move laterally once inside?
Can we prove our backups actually recover — not just that they exist?
Can we prove our monitoring would actually catch an attack in progress?
And then, the twist
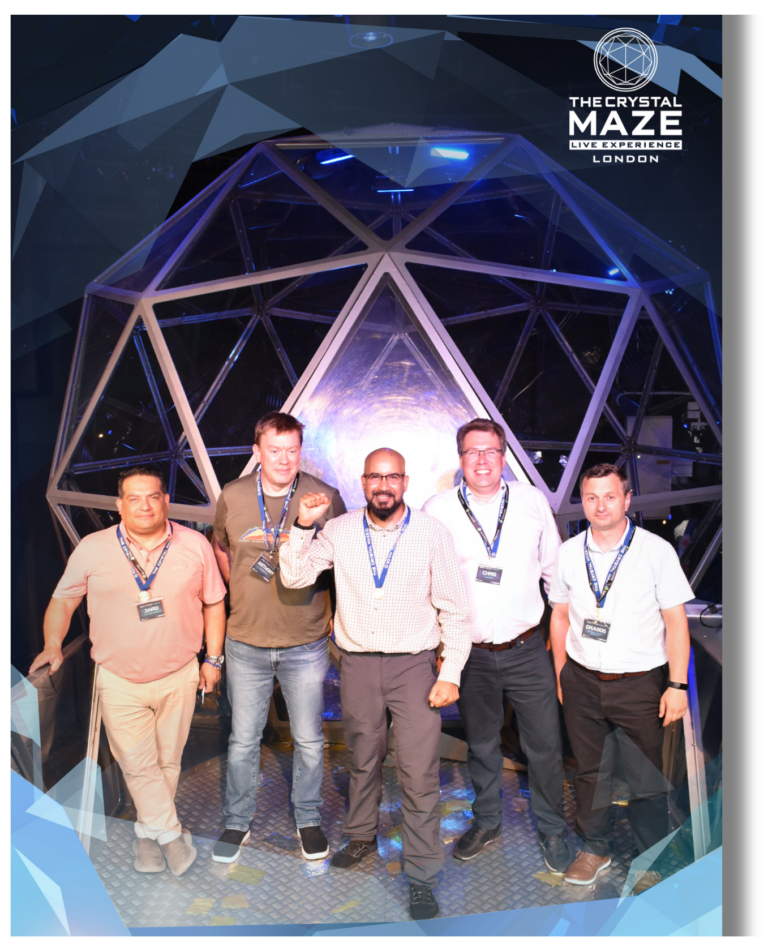
Into The Crystal Maze
Teams stepped into the maze to test their communication, problem-solving, and teamwork under pressure. From tackling challenges to adapting on the move, the experience highlighted the importance of staying calm and thinking strategically.
- Well Done our winners!
Watch The Highlights
AI in Cyber Attacks: What We’re Actually Seeing
How Hackers Get Around Your Security Tools | Lessons From 220+ Ransomware Attacks
Inside the Breach · Vol. VII · Crystal Maze London · July 2026
Next Upcoming Event...
14
th
Oct 2026
Crystal Maze Live Experience
Inside The Next Breach: Understanding the AI Threat Before It Lands
Would your team hold it together when the systems go down? A free half-day for IT and business leaders on the AI threat, plus the iconic Crystal Maze.
Vol. VI - SyscommxIBM - Defending Your Data Event at IBM HQ Apri 2026