Modern businesses rely on an increasingly interconnected network of technology. From email and cloud platforms to security systems, business applications and data storage, each plays an important role in keeping organisations operational. But what happens when one of those services suddenly becomes unavailable?
Last week’s widespread Microsoft 365 outage provided a timely reminder of just how dependent businesses have become on the technology they use every day. Beginning on Thursday 12 November, the disruption affected Outlook, Teams, Copilot and other Microsoft services, leaving organisations across the world struggling to access tools essential to their daily operations.
The outage lasted more than 24 hours, with Microsoft confirming on Saturday 14 November that services had fully recovered. While the company reported no evidence of malicious activity, the incident raised an important question for organisations everywhere: how resilient is your business when the technology it depends on stops working?
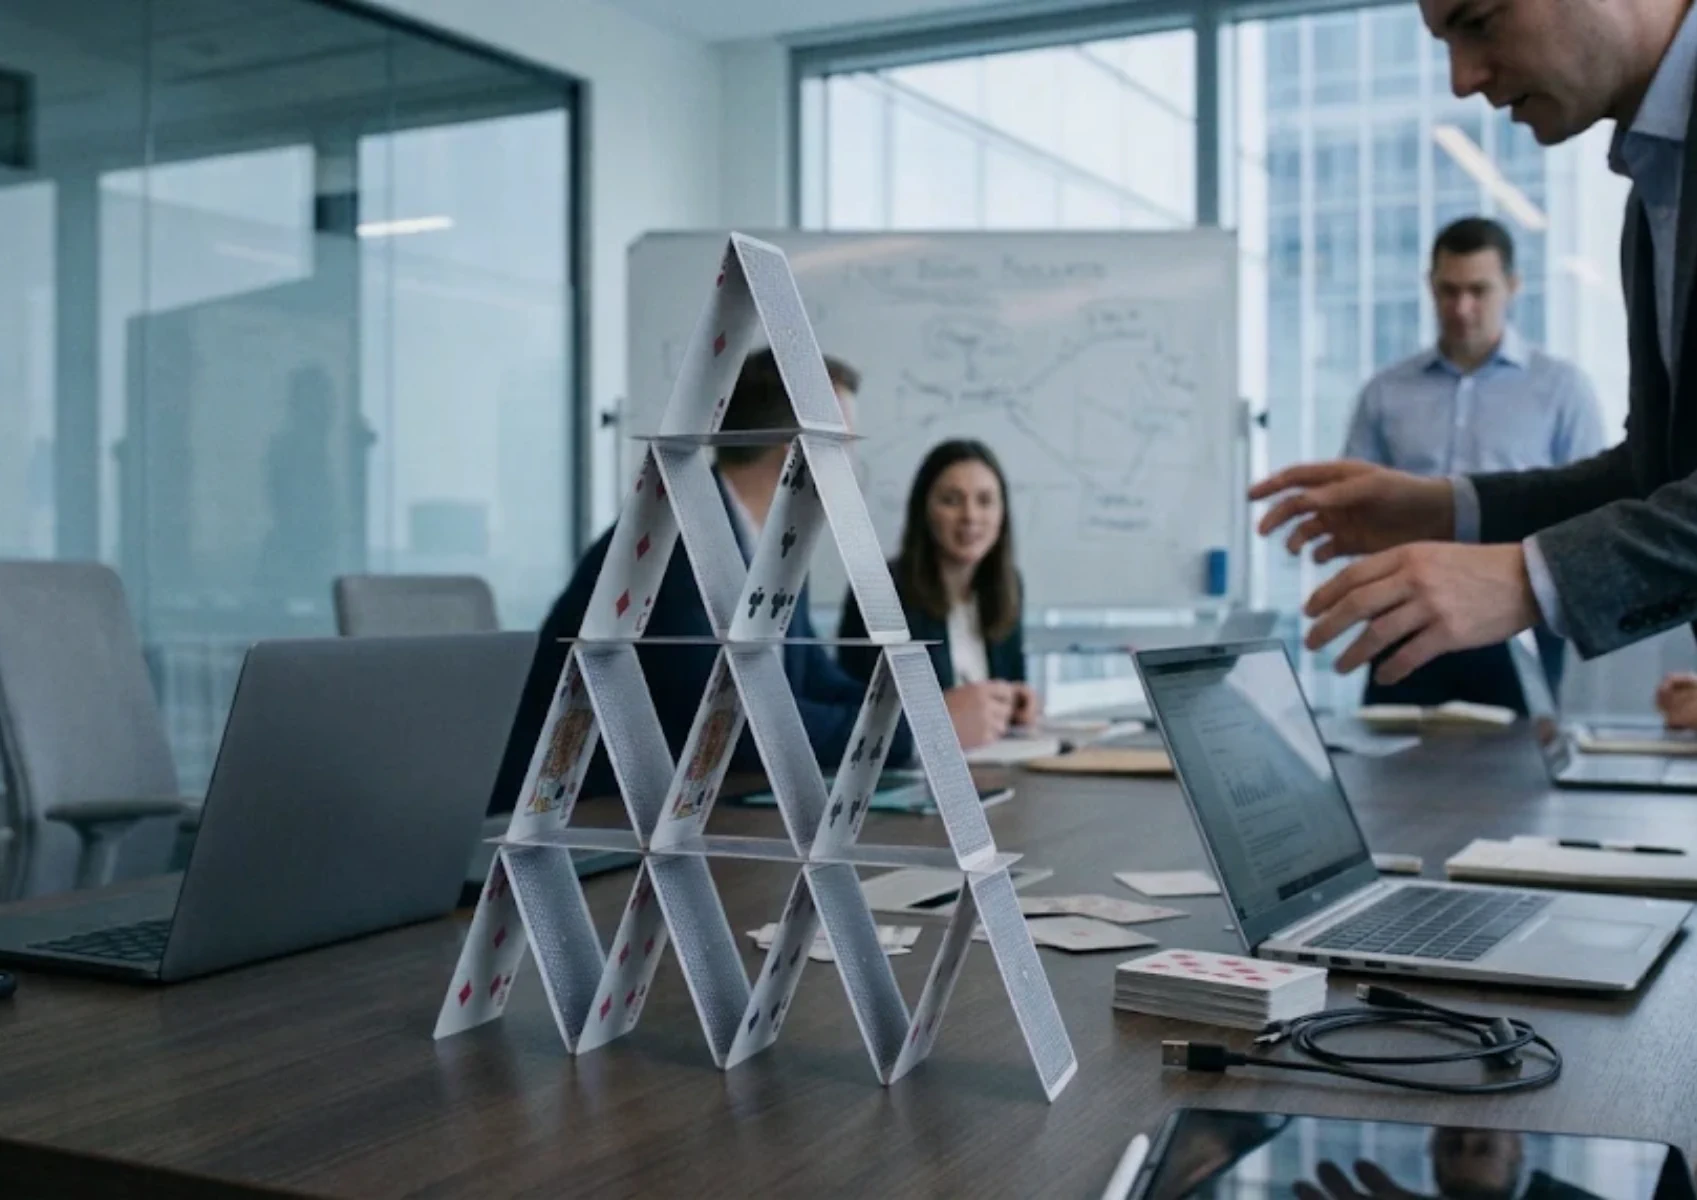
The house of cards behind modern IT
IT environments are rarely made up of completely independent systems. Instead, they operate through layers of interconnected services, platforms and infrastructure. Consider a typical working day, employees access their devices using identity services, communicate through Microsoft 365, retrieve files from cloud storage, use business applications and rely on security tools to monitor activity across their environment.
Each component has a purpose, but many also depend on something else working correctly. This creates a web of dependencies that isn’t always obvious until something goes wrong. Think of it like a house of cards. Each component might appear stable on its own, but the wider structure relies on everything supporting everything else. Remove one important element and the impact can extend much further than expected.
The recent Microsoft outage demonstrated how disruption at a major technology provider can affect organisations far beyond the service experiencing the initial problem. According to Reuters’ coverage of the incident, the disruption affected businesses and government organisations across multiple countries, highlighting the extent to which essential communications and operations rely on a relatively small number of technology providers.
And Microsoft isn’t the only example. Businesses increasingly rely on external cloud providers, internet connectivity, software platforms and third-party suppliers to keep their operations running. The question isn’t whether these services are valuable. It’s whether organisations understand what happens when they become unavailable.
Reliability isn’t the same as resilience
Cloud services offer significant advantages, including scalability, accessibility and reduced infrastructure management. However, using a reputable provider doesn’t remove the need for an organisation to consider its own continuity arrangements. There is an important distinction between the reliability of a service and the resilience of the business using it.
A provider may have extensive infrastructure, monitoring and recovery arrangements in place. But that doesn’t automatically mean your organisation has a plan for operating when that service is unavailable.
For example:
- Can employees continue communicating if your primary email platform is inaccessible?
- Do you have alternative ways to access essential business information?
- Which operations would stop if your identity or authentication services became unavailable?
- Do you understand which business applications depend on the same underlying systems?
- How would your organisation continue serving customers during a prolonged disruption?
These aren’t simply technical questions. They’re business continuity questions. The National Cyber Security Centre’s guidance on preparing business continuity plans recommends that organisations identify their critical services, understand the technology and suppliers supporting them, and consider practical workarounds if those services become unavailable. This is particularly important because the impact of an outage isn’t always limited to the time a service is offline. Missed communications, delayed decisions, interrupted processes and backlogs can continue to affect an organisation long after systems are restored.
Disaster recovery: Planning for more than a cyber attack
Disaster recovery is often discussed in the context of ransomware, data loss or physical infrastructure failure. But the underlying principle is broader: organisations need to understand how they will recover when something they depend on is disrupted. Not every incident will look the same, and not every incident will be within your organisation’s control. A provider-side outage, a network failure, a hardware fault and a cyber attack all have different causes. However, each can raise similar questions about availability, dependencies and the ability to continue operating.
A good disaster recovery strategy should consider several important areas.
1. Identify what your business cannot operate without
Start by identifying your critical systems and services. Consider not only the applications employees use, but also the infrastructure and third-party services that support them. Understanding which systems are essential, and how long your organisation can operate without them, helps establish where recovery efforts should be prioritised.
2. Understand your dependencies
Map how your systems connect. If your email, file storage and business applications all rely on the same identity service or network infrastructure, understand what happens if that dependency becomes unavailable. Without a clear picture of these relationships, organisations can overlook vulnerabilities that only become apparent during disruption.
3. Have a plan for operating during disruption
Consider alternative communication methods, manual processes and temporary workarounds. These should be practical, understood by employees and appropriate for the information being handled. Having an alternative process is only useful if people know when and how to use it.
4. Protect your data and understand your recovery options
Backups remain an essential part of recovery planning, particularly when dealing with data loss or ransomware. However, having backups isn’t enough. Organisations need to know that they can restore the data, applications and configurations they depend on. The NCSC’s technical recovery guidance recommends maintaining secure, tested backups and planning restoration processes that account for applications, identity systems and infrastructure dependencies.
5. Test your plans
A recovery plan that has never been tested is largely an assumption. Regular exercises can help identify gaps, establish responsibilities and highlight issues before an actual incident occurs. This includes testing whether backups can be restored, whether alternative processes work and whether the right people understand their responsibilities. The NCSC also recommends regularly testing and exercising business continuity and recovery plans to identify weaknesses that might otherwise only become apparent during a real incident.
You cannot prevent every outage. You can prepare for the impact.
The recent Microsoft disruption is a useful reminder that even widely used, established technology platforms can experience problems. No organisation can guarantee that every service it relies on will always be available. Nor is it realistic to expect businesses to eliminate every external dependency. But organisations can take steps to understand those dependencies, reduce unnecessary single points of failure and prepare for the consequences when something goes wrong.
The aim of disaster recovery isn’t simply to get everything back online as quickly as possible. It’s to ensure that when disruption happens, the business knows what matters most, what needs to happen next and how to restore operations in a controlled way. Because a resilient IT environment isn’t one where nothing ever goes wrong. It’s one that is prepared when something does.
Does your organisation know what would happen if one of its most important IT services became unavailable tomorrow?
At Syscomm, we help organisations strengthen their IT environments, improve cyber resilience and plan for disruption. Understanding where your dependencies lie is an important first step towards building an environment that can withstand the unexpected.