How Cyber Resilient Is Your College or University? 7 Questions IT Leaders Should Ask
Education relies on digital systems to deliver teaching, manage student records, support research and keep day-to-day operations running. But how prepared is your institution if those systems suddenly become unavailable? Cyber security is no longer just about preventing attacks. It is also about limiting their impact, recovering essential services and maintaining continuity when something goes […]
PHP2Shell: What organisations need to know about two critical PHP vulnerabilities
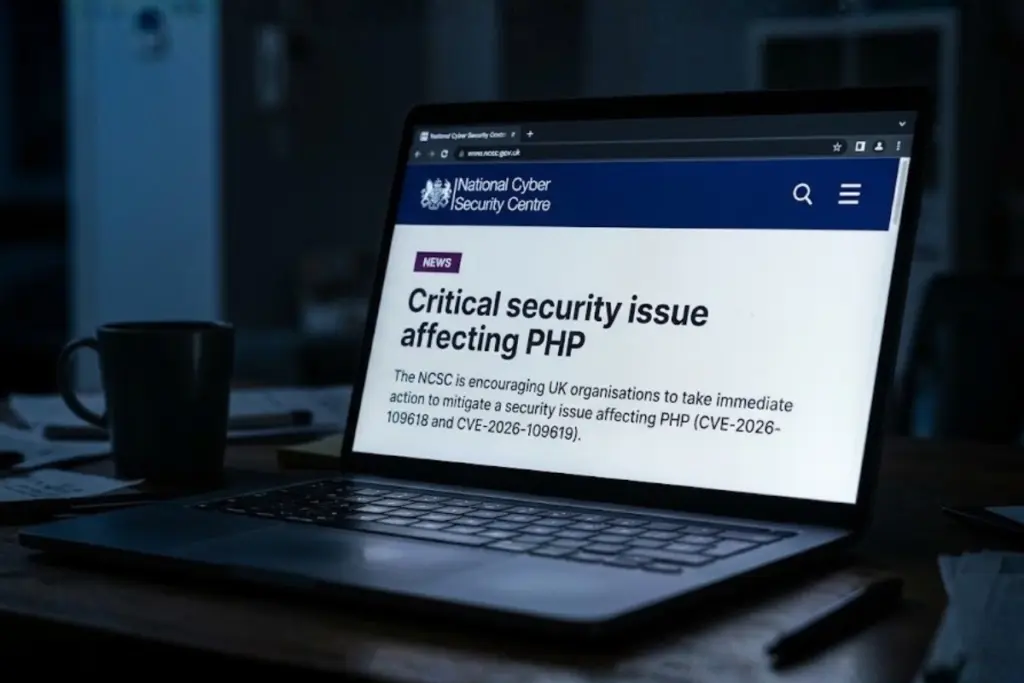
Two critical vulnerabilities affecting PHP have prompted an urgent security alert. Disclosed on 21 October 2026, CVE-2026-109618 and CVE-2026-109619, collectively known as PHP2Shell, could allow unauthenticated attackers to execute code remotely on vulnerable servers. Both vulnerabilities have a CVSS v4.0 score of 9.2 out of 10, placing them in the critical severity category. Successful exploitation […]
Would You Know If an Attacker Was Already Inside Your Network?
You have a firewall and security tools in place. But if an attacker had already gained access to your network, would you know? Cyber attacks aren’t always obvious. Attackers can use stolen credentials or exploit system weaknesses to move through a network undetected, potentially accessing sensitive data or critical systems before anyone notices.The challenge isn’t […]
How Do Cyber Attacks Actually Happen?
Cyber attacks can sometimes seem like a distant or highly technical threat. But behind every successful attack is a sequence of events. An attacker needs to find a way in, gain access, and ultimately achieve their objective. What happens between those points can vary significantly and understanding that journey is an important part of building […]
5 Ways AI Is Changing the Cyber Threat Landscape
Artificial intelligence is changing the way organisations work, but it is also changing the way cyber criminals operate. The important point is that AI isn’t necessarily creating completely new types of cyber attack. Instead, it is helping attackers make existing techniques faster, more scalable and more effective. The UK’s National Cyber Security Centre (NCSC) has […]
Building a Smarter, More Secure Network with Extreme Networks
The network is no longer simply the infrastructure that connects people to the internet. For modern organisations, it sits underneath almost everything: cloud applications, collaboration tools, security systems, wireless devices, IoT, remote working and increasingly, artificial intelligence. As organisations become more connected, the demands placed on their networks are changing too. Networks need to support […]
You Have Cyber Insurance. That Doesn’t Mean You’re Covered.
Having cyber insurance is not the same as being covered: a policy won’t stop the downtime, the lost contracts or the reputational damage, and insurers decline to pay more often than boards expect. The businesses that survive an attack treat insurance as a backstop, not a plan, and can answer the right questions long before they need to claim. […]
Help Desk Impersonation Attacks: The Social Engineering Threat Organisations Need to Know
Imagine receiving a phone call from someone claiming to be from your IT team. They know your name, your job role and even mention a problem with your account. They ask you to approve a multi-factor authentication (MFA) request or install remote support software so they can “fix” the issue. It sounds convincing. That’s exactly […]
The Configuration Gap: Why Having the Right Tools Isn’t Enough
Most businesses hit by ransomware already own the right security tools. The breach comes from what is unpatched, misconfigured or poorly segmented behind them, and since no one can patch everything, the businesses that recover fastest are the ones designed to contain an intrusion, not just keep it out. Every operational business we have recovered […]
What Is IASME Cyber Assurance and Why Does It Matter?
Cyber security has become a critical priority for organisations of all sizes. As businesses become increasingly dependent on cloud platforms, connected systems and digital services, the potential impact of a cyber incident continues to grow. Many organisations have invested in security technologies such as firewalls, endpoint protection, backup solutions and monitoring tools. However, having security […]